Deploy your model anywhere. Expose nothing.
Your trained model runs on customer sites, edge devices and partner clouds, and it is never decrypted there. There is nothing to copy, dump or walk away with.
Three places your model goes
Your model earns money outside your walls. That is where it is exposed.
- 01
Customer sites
The weights stay encrypted while the model runs.
Today: A licensed model is decrypted into memory on the customer's server.
- 02
Edge devices
A memory dump yields ciphertext.
Today: Anyone holding the device can dump memory or pull the storage.
- 03
Partner clouds and delivered systems
Possession of the system does not give possession of the model.
Today: A privileged admin or a teardown can recover the model.
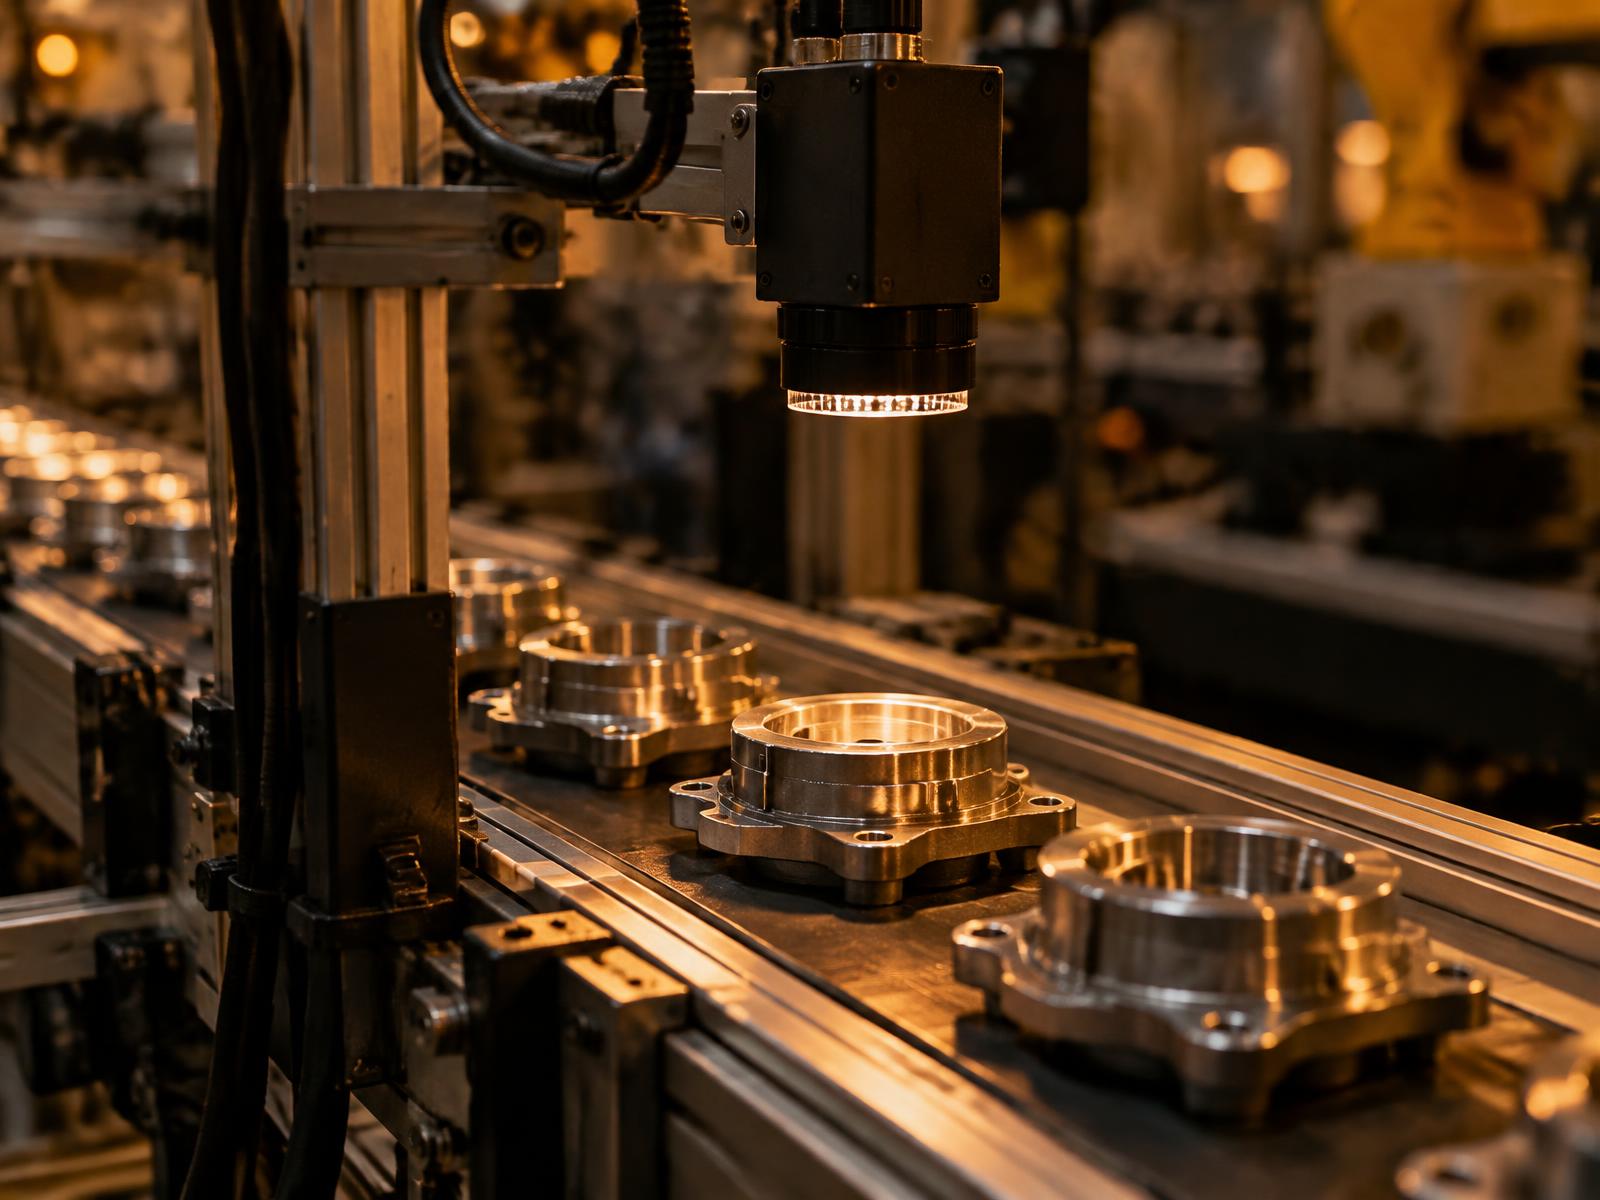
Your model ships inside someone else's machine.
Defect detection and inspection classifiers on industrial PCs and customer lines stay encrypted while they run.
- OEM machines
- Industrial PCs
- Customer lines
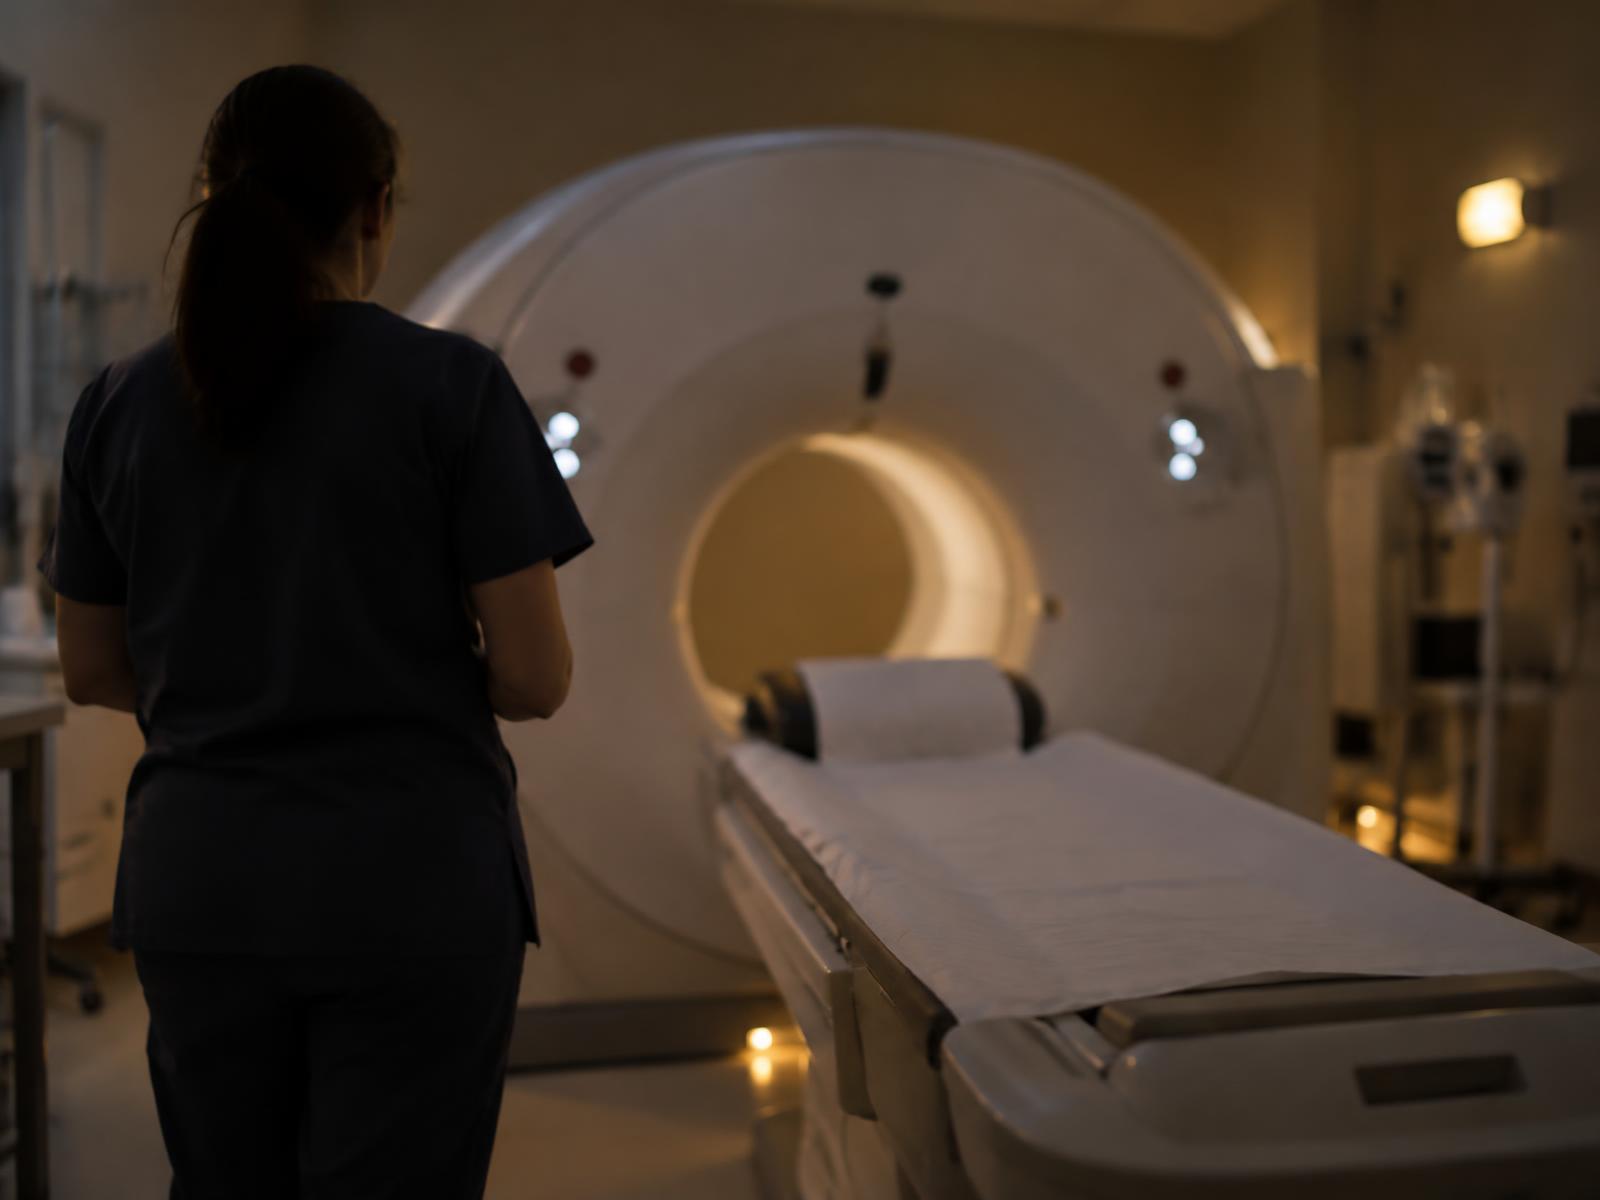
Your model is installed in the hospital.
Run per-study inference on the hospital's own infrastructure. Patient data stays on site. Your weights are never decrypted there.
- On premises
- Per-study inference
- Beside PACS
How it works in four steps
How it works in detail- 01
Encrypted model
Your ONNX or TensorRT model, converted to ciphertext
- 02
Dropnir gateway
A Docker container, no enclave required
- 03
Customer hardware
Site, edge device or partner cloud
- 04
Owner-controlled result
You hold the key to decrypted outputs
The honest comparison
Every figure we give you states its conditions: model, input size, hardware, batch size.
| Aspect | Licensing and dongles | Hardware enclaves | Encrypted inference |
|---|---|---|---|
| Weights at rest | Encrypted | Encrypted | Encrypted |
| Weights during inference | Decrypted in memory | Plaintext inside the enclave | Stay encrypted |
| Physical possession of the box | Model recoverable from memory | Relies on physical security | Yields ciphertext |
| Hardware requirements | Dongle or licence server | Specific CPU or GPU with enclave support | No enclave required |
Why model IP is on the table now
Industrial AI
AI can reverse-engineer your software. What protects your model?
Coding agents can now trace how a shipped program works. If your model ships with it, the weights deserve their own answer.
Read the article
Defence research
When the hardware is captured, what happens to the model?
On-device autonomy puts trained models on hardware that can be lost or recovered. Jamming resilience and model confidentiality are separate questions.
Read the article
Medtech
Your medical AI leaves the lab. Does your model IP leave with it?
Threat intelligence now reports proprietary AI models stolen from a healthcare organisation. Vendors installing on premises should ask where their weights sit.
Read the article
Bring one model and one target.
We tell you what it costs in latency and what it buys in protection.